Post Date: July 03, 2018
Last Updated: November 21, 2026
Introduction
By default, cPanel servers use iptables to manage inbound and outbound connections. iptables checks rules one after another, so a very large block list (thousands of IPs) can slow the server and hurt network performance.
IPSET solves this. It stores IP addresses in a hash-based set, and iptables checks the whole set with a single rule. CSF (ConfigServer Security & Firewall) supports IPSET through one setting, so you can block large lists without the slowdown.
Prerequisites
- Root SSH access to the cPanel server
- CSF already installed
- A server that is not running on Virtuozzo or OpenVZ. IPSET is not supported on those kernels, so if your cPanel server sits behind either one, skip this setup.
Architecture
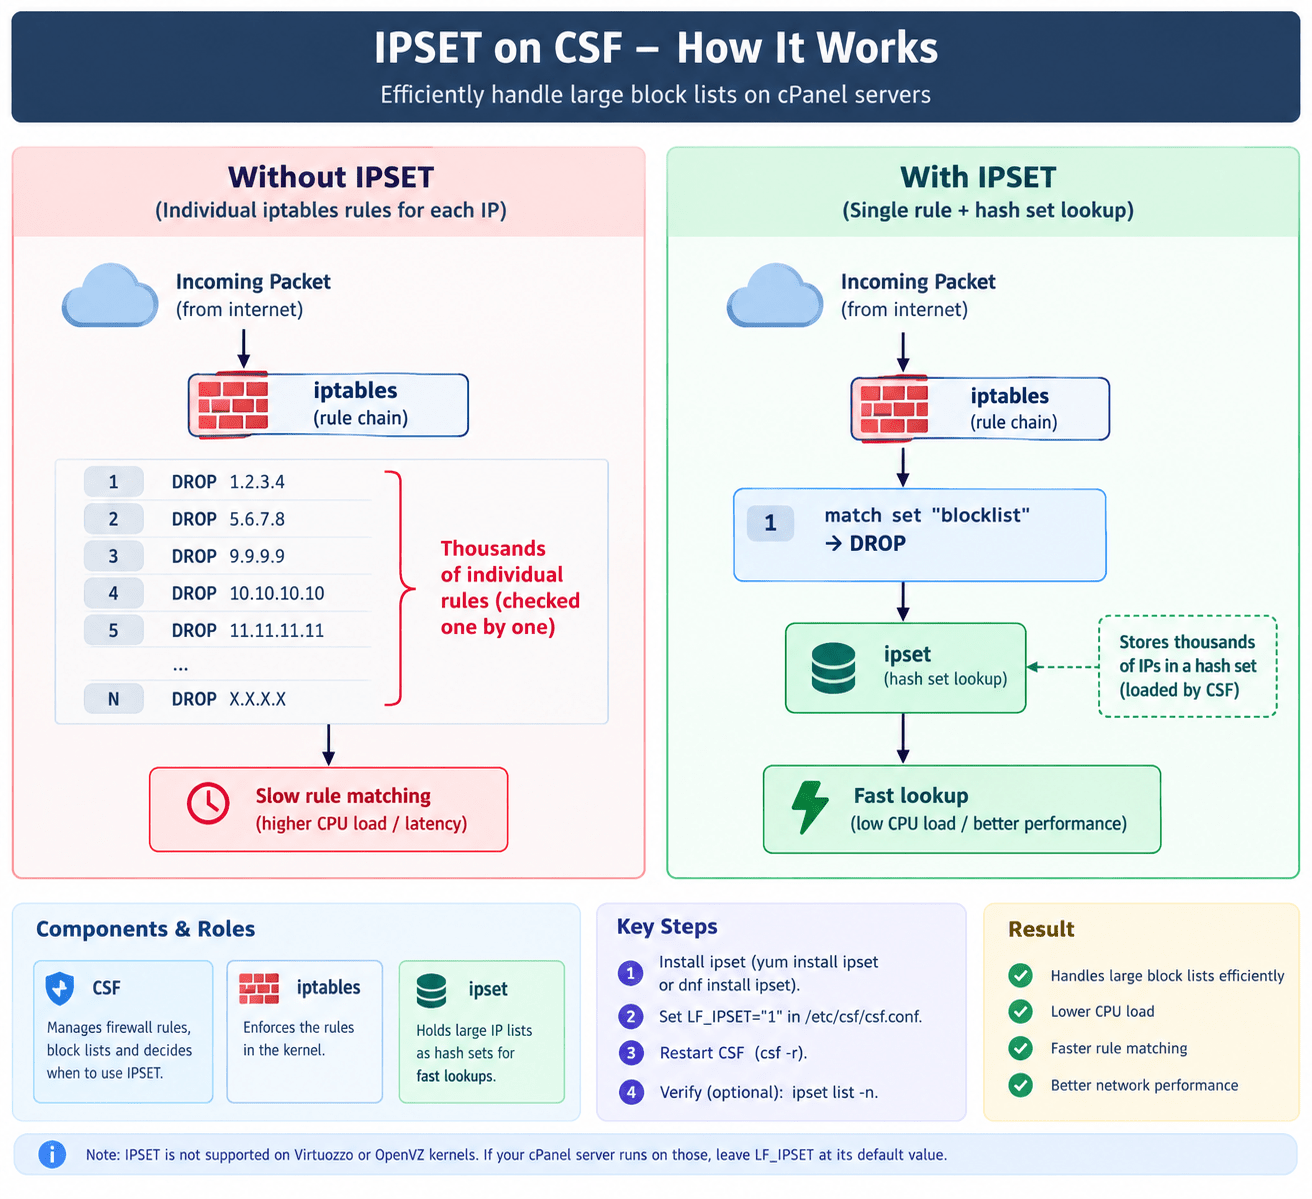
Without IPSET, every IP in your deny list becomes its own iptables rule, and each packet is compared against them in order. With IPSET, CSF loads the IPs into a set and iptables uses one rule to match against it.
| Component | Role |
|---|---|
| CSF | Manages firewall rules and block lists, and decides when to use IPSET |
| iptables | Enforces the rules in the kernel |
| ipset | Holds large IP lists as hash sets for fast lookups |
Steps
Step 1: Log in to the server via SSH as root.
Step 2: Install ipset.
yum install ipset
On newer cPanel servers running AlmaLinux or Rocky Linux, use dnf install ipset instead.
Step 3: Open the CSF configuration file.
vi /etc/csf/csf.conf
Step 4: Find the LF_IPSET parameter and set it to 1.
LF_IPSET="1"
Step 5: Save and exit the file using :wq!.
Step 6: Restart CSF so the change takes effect.
csf -r
Step 7 (optional): Verify the setup. List the sets to confirm CSF created them.
ipset list -n
Conclusion
IPSET lets CSF handle large block lists efficiently instead of adding thousands of individual iptables rules. On a busy cPanel server this means lower CPU load, faster rule matching, and better network performance. The setup is a package install, one setting change, and a CSF restart.
FAQ- Frequently Asked Questions
What is IPSET? A Linux kernel feature that stores IP addresses, networks, or ports in sets, so iptables can match against thousands of entries with a single rule.
Does IPSET work on Virtuozzo or OpenVZ? No. Those kernels don’t support it, so leave LF_IPSET at its default on such servers.
Will my existing blocked IPs be lost after enabling IPSET? No. CSF reloads your allow and deny entries into IPSET when it restarts with csf -r.
How do I know IPSET is working? Run ipset list -n after restarting CSF. If sets appear, IPSET is active.
How do I turn it off? Set LF_IPSET="0" in /etc/csf/csf.conf and run csf -r.
Related Articles
How to Manage the CSF Firewall in WHM/cPanel
Increase the LFD 5-Minute Load Average Alert Threshold in CSF
Talk to our experts
Need help securing or optimizing your cPanel server? The PheonixSolutions team can configure CSF, tune your firewall, and keep your servers running smoothly. Contact us today.