Introduction
Trivy is an open-source vulnerability scanner for containers, filesystems, and Git repositories. It detects vulnerabilities, misconfigurations, and security issues in container images, packages, and infrastructure as code, and is widely used in DevOps pipelines for continuous security checks.
Implementation
I. Prerequisites
- Ubuntu/Debian-based Linux distribution
- Root or sudo privileges
wget,apt-transport-https, andgnupgavailable- Internet access to reach Trivy’s official repository
II. How Trivy Fits Into Your Pipeline
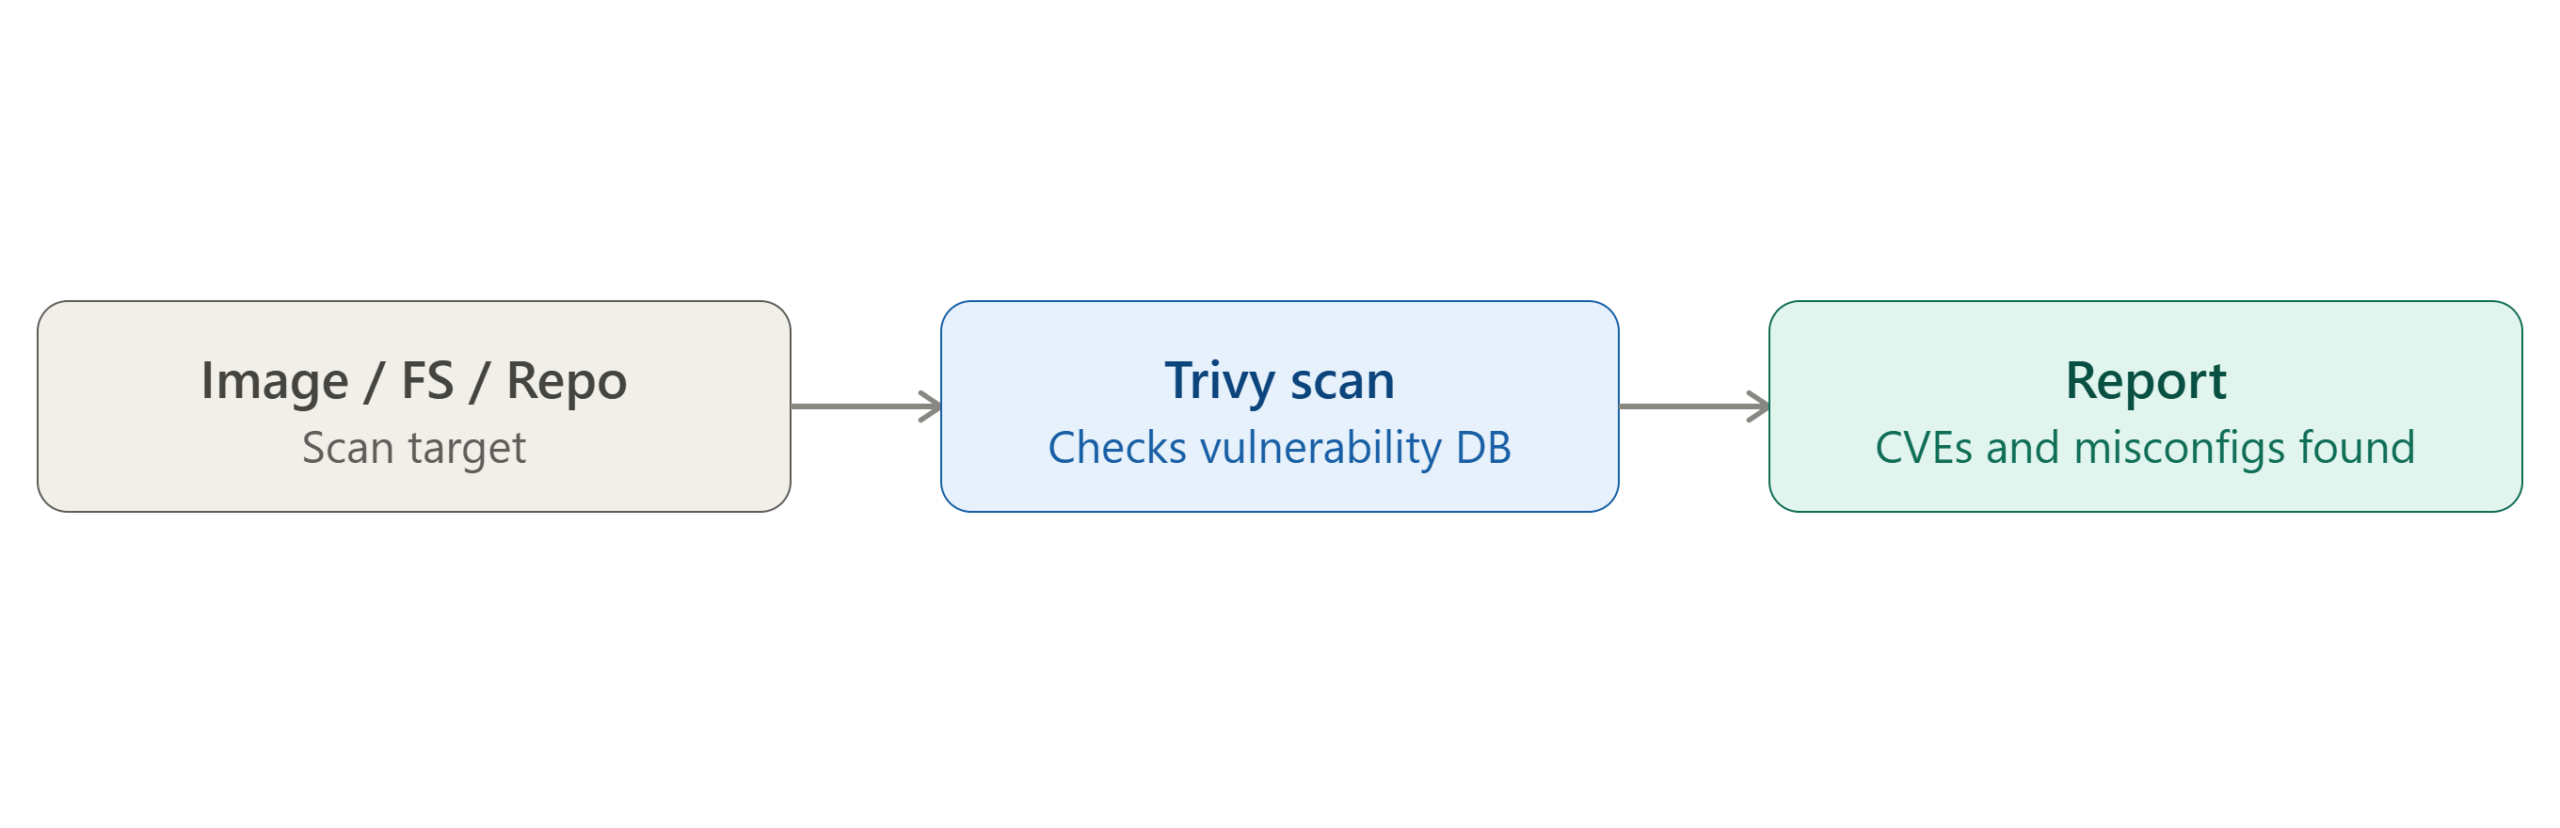
- Trivy scans a target — a container image, filesystem path, or Git repository
- It checks that target against vulnerability databases it downloads and keeps updated
- It reports back any known CVEs, misconfigurations, or exposed secrets it finds
III. Install Dependencies
sudo apt-get update
sudo apt-get install -y wget apt-transport-https gnupg lsb-release
This installs wget (download files), apt-transport-https (HTTPS repositories), gnupg (verify signatures), and lsb-release (detect your OS version).
IV. Add the Trivy GPG Key
wget -qO - https://aquasecurity.github.io/trivy-repo/deb/public.key | sudo gpg --dearmor -o /usr/share/keyrings/trivy.gpg
Note: The original method (
apt-key add) is deprecated and has been removed entirely on current Ubuntu/Debian versions. The command above uses the current recommended approach — storing the key as a dedicated keyring file and referencing it explicitly in the repository entry (Step V), rather than adding it to a shared system-wide keyring.
V. Add the Trivy Repository
echo "deb [signed-by=/usr/share/keyrings/trivy.gpg] https://aquasecurity.github.io/trivy-repo/deb $(lsb_release -sc) main" | sudo tee /etc/apt/sources.list.d/trivy.list
The signed-by flag tells apt to verify this specific repository using the keyring file from Step IV, rather than trusting any key in the system’s general keyring — a more secure, explicit approach than the older method.
VI. Install Trivy
sudo apt-get update
sudo apt-get install -y trivy
VII. Verify Installation
trivy -v
This confirms Trivy installed correctly and shows the installed version.
VIII. Conclusion
Trivy installs cleanly through its official APT repository, with the current setup using an explicit signed-by keyring reference instead of the deprecated apt-key method. Once installed, you can scan container images, filesystems, or repositories directly:
trivy image <image_name>
trivy fs <path_to_filesystem>
Frequently Asked Questions
Why was apt-key replaced? apt-key trusted keys system-wide for all repositories, which was a broader security surface than necessary. The signed-by approach scopes each key to just the specific repository it’s meant to verify.
Can Trivy scan private container registries? Yes — Trivy supports authenticating against private registries using standard Docker credential mechanisms.
Does Trivy need internet access every time it runs? It needs access to update its vulnerability database periodically, but can run scans using a cached database if offline, as long as the database was downloaded previously.
Related Articles
How to Renew Kubernetes Certificates Using kubeadm (Step-by-Step Guide with Zero Planned Downtime)
How to Configure cert-manager ClusterIssuer with Cloudflare API Token on Kubernetes
Talk to our experts.
Looking for the right technology solution for your business? Our team of experts can help you with development, cloud, DevOps, design, and a wide range of other technology needs. Get in touch with our team here.