Post Date: March 24, 2017
Last Updated: November 02, 2026
Introduction
Hide webserver information in Nginx to reduce unnecessary information disclosure through HTTP response headers. By default, Nginx may expose its server version, which can provide attackers with additional details about your webserver environment.
Nginx provides the server_tokens off; directive to hide version information. If you also want to customize the Server response header, you can use the third-party headers-more module. For more information, refer to the official Nginx server_tokens documentation.
Hiding webserver information is an important step in Nginx security hardening. When you hide webserver information, you reduce the amount of technical details exposed through HTTP response headers. This helps prevent visitors from identifying the exact Nginx version running on your server.
In this guide, we will explain how to hide the Nginx version, install the required module, modify the Server header, and verify the changes using curl.
Prerequisites
Before proceeding, make sure you have:
- An Ubuntu or CentOS server.
- Root or sudo access to the server.
- Nginx installed and configured.
- Basic knowledge of Nginx configuration.
If Nginx is not installed, refer to the appropriate installation guide:
Note: The configuration described in this article was tested on Ubuntu. The
more_set_headersdirective requires the Nginx headers-more module, which may need to be installed separately depending on your Nginx package.
Implementation
In this implementation, we will configure Nginx to hide webserver information and customize the Server response header. We will use the server_tokens directive to disable version disclosure and the headers-more module to set a custom Server header. Finally, we will verify the changes using the curl command.
Step 1: Install the Required Nginx Package
On Ubuntu, install nginx-extras:
apt-get -y install nginx-extras
The nginx-extras package provides additional Nginx modules, including the functionality required for the more_set_headers directive.
Step 2: Check the Current Server Information
Before configuring Nginx to hide webserver information, inspect the existing HTTP response headers using the curl command. This helps identify whether the Nginx version and operating system details are currently exposed to clients.
Run:
curl -I http://IPaddress
You may see output similar to:
HTTP/1.1 301 Moved Permanently
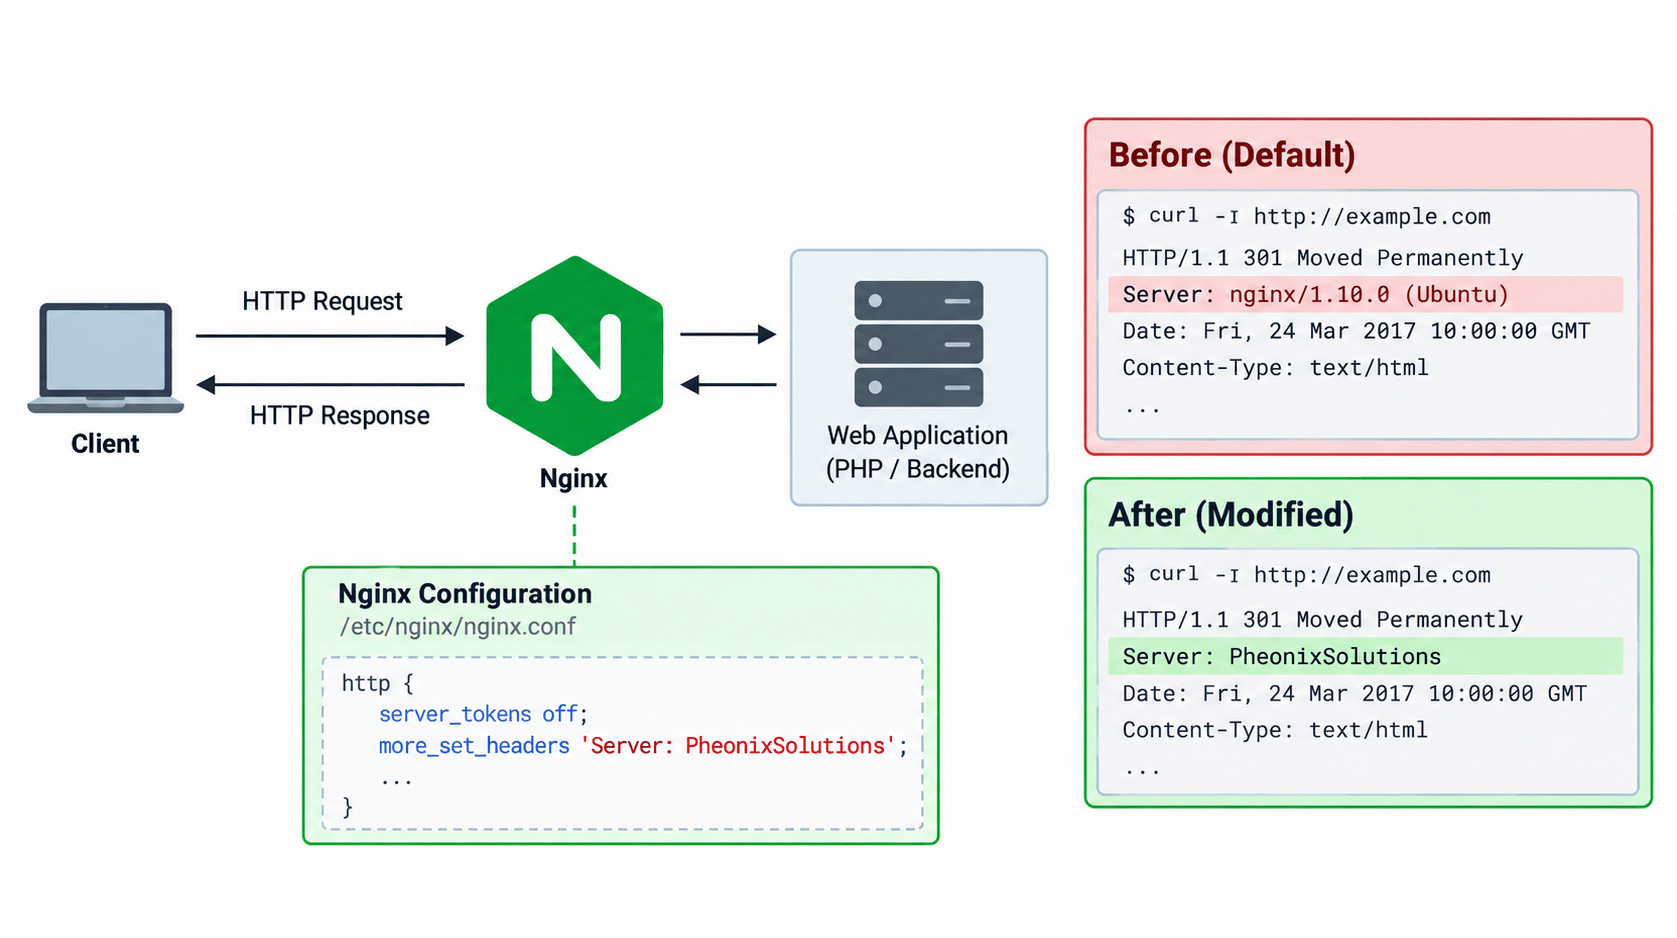
Server: nginx/1.10.0 (Ubuntu)
The Server header reveals both the Nginx version and operating system information.
Step 3: Modify the Nginx Configuration
To hide webserver information in Nginx, configure the server_tokens off; directive inside the HTTP context. This disables version disclosure in the Server response header. If you want to replace the default Server header, configure the headers-more module separately.
Open the Nginx configuration file:
vi /etc/nginx/nginx.conf
Under the http section, add or modify the following configuration:
server_tokens off;
more_set_headers 'Server: PheonixSolutions';
The server_tokens off; directive prevents Nginx from including its version number in the Server header.
The more_set_headers directive allows you to replace the default Server header with a custom value.
For example:
http {
    server_tokens off;
    more_set_headers 'Server: PheonixSolutions';

    ...
}
Step 4: Test the Nginx Configuration
Before restarting Nginx, check the configuration for syntax errors:
nginx -t
A successful configuration test should return:
syntax is ok
test is successful
Step 5: Restart Nginx
Restart the Nginx service:
service nginx restart
Alternatively, on systems using systemd:
systemctl restart nginx
Step 6: Verify the Server Header
After restarting Nginx, verify that the configuration works as expected. Successfully hiding webserver information should prevent the Nginx version from appearing in the response header. If you configured a custom Server header, confirm that the response displays your chosen value.
Run the same curl command again:
curl -I http://IPaddress
The response should now contain a custom Server header similar to:
HTTP/1.1 301 Moved Permanently
Server: PheonixSolutions
The Nginx version and operating system information are no longer exposed in the response header.
Conclusion
By default, Nginx can expose server version information through HTTP response headers. Disabling server_tokens helps prevent Nginx from revealing its version, while the headers-more module can be used to customize the Server header.
Although hiding server information is not a complete security solution, reducing unnecessary information disclosure is a useful security hardening practice.
FAQs
1. Why should I hide the Nginx version?
Exposing the Nginx version provides unnecessary information about the server and may help attackers identify vulnerabilities associated with a particular version.
2. What does server_tokens off do?
The server_tokens off; directive prevents Nginx from displaying its version number in the Server response header.
3. Does server_tokens off completely remove the Server header?
No. It normally hides the version information but does not remove the Server header itself.
4. How do I hide webserver information in Nginx?
You can hide webserver information by setting server_tokens off; in the Nginx HTTP configuration. To customize or remove the Server response header, use the headers-more module.
Related Article
Install Nginx on cPanel Using Engintron (Step-by-Step Guide)
How to install and configure PHP with Nginx on centos7 – Pheonix Solutions
Strengthen Your Nginx Security with Expert Protection
Want to harden your web servers and reduce the information they expose? Our team can review your Nginx setup, close security gaps, and keep your infrastructure protected with our Security Services.
Connect with our technology experts.