Post Date: May 18, 2020
Last Updated: November 12, 2026
Introduction
This guide explains how to block IPs via htaccess on an Apache web server. An .htaccess file lets you deny single IP addresses, whole ranges, or everyone except a trusted few. You can apply the rules to a whole site or to one folder, without editing the main Apache configuration.
The original guide used the old Order, Allow and Deny directives from Apache 2.2. Those still work on Apache 2.4 only if a compatibility module is loaded. This version uses the current Require syntax and keeps the old syntax as a fallback. It also fixes the example IP 290.0.0.0, which is invalid because no part of an IPv4 address can exceed 255. A lockout warning and troubleshooting section are new too.
Warning: When you block IPs via htaccess, a wrong rule can lock you out of your own site. Back up the file first, and keep your own IP in an allow list if you work on a restricted folder. A syntax error in
.htaccessreturns a 500 Internal Server Error for the whole directory.
Prerequisites
Before you block IPs via htaccess, make sure you have:
- File Manager, FTP or SSH access to the site’s folder
- Apache as the web server (LiteSpeed also reads
.htaccess, but Nginx does not) AllowOverride All(or at leastAllowOverride AuthConfig Limit) set for the folder, otherwise Apache ignores the file- The IP addresses you want to block, and your own IP so you don’t block yourself
- A backup copy of any existing
.htaccessfile
Architecture
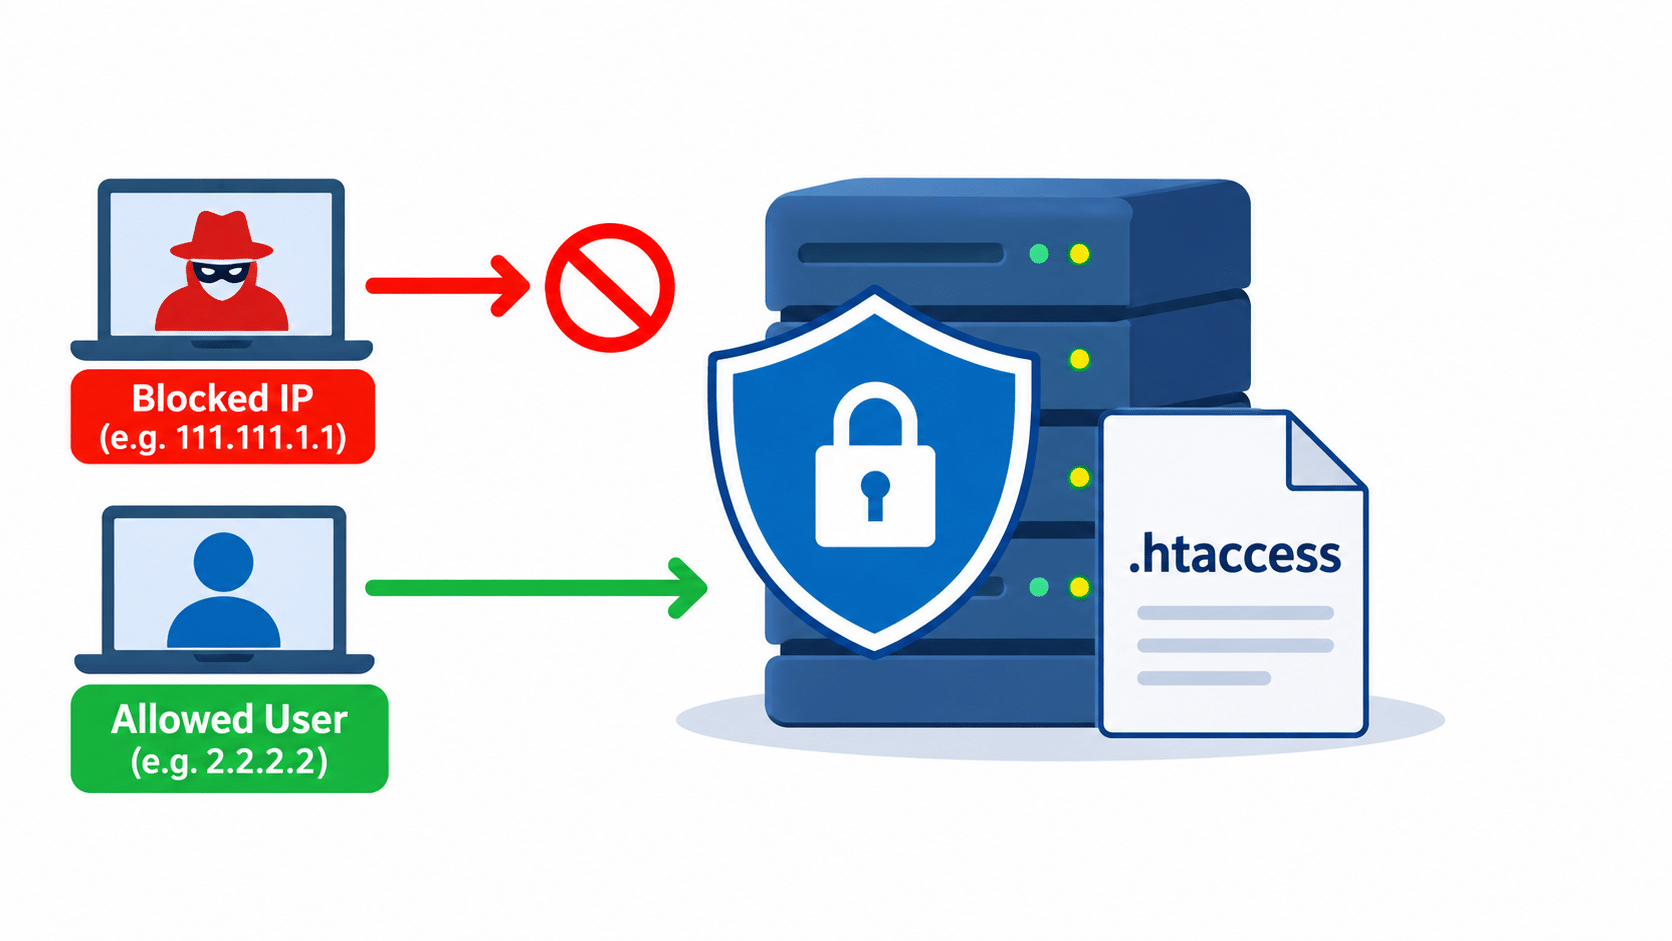
- A visitor’s request reaches Apache, which sees the visitor’s IP address
- Apache reads the
.htaccessfile in the requested folder and in each parent folder up to the document root - The access rules compare the visitor’s IP with your
Requirelines (or the oldAllowandDenylines) - A match on a blocked address returns 403 Forbidden, and any other visitor gets the page with 200 OK
- The
.htaccessfile inpublic_htmlcovers the whole site, and one inside a subfolder covers only that folder
The image below shows the workflow. For the official reference, see the Apache guide on access control and the .htaccess how-to.
Steps to Block IPs via htaccess on Apache
Short answer: To block IPs via htaccess on Apache 2.4, open or create the .htaccess file, wrap Require all granted and one Require not ip line per address inside a <RequireAll> block, save the file, and test that a blocked IP gets a 403 error. On Apache 2.2, use Order allow,deny with Deny from lines.
1. Check Your Apache Version and Find the File
apachectl -v
.htaccess is a hidden file because of the leading dot. Turn on “Show Hidden Files” in File Manager or your FTP program. If the file does not exist, create it:
- Whole site: put
.htaccessin thepublic_htmlfolder - One folder: put it inside that folder, for example
public_html/devto protecthttps://example.com/dev
Back up an existing file before editing:
cp .htaccess .htaccess.bak
2. Block Specific IP Addresses (Apache 2.4)
This is the core step to block IPs via htaccess. Add one Require not ip line per address:
<RequireAll>
    Require all granted
    Require not ip 203.0.113.10
    Require not ip 198.51.100.7
</RequireAll>
The original examples used 290.0.0.0 and 111.111.1.1. These examples use reserved documentation addresses, so replace them with the real IPs you want to block. To block more, add more Require not ip lines inside the block.
3. Block a Whole IP Range
Use CIDR notation or a partial address to block a range:
<RequireAll>
    Require all granted
    Require not ip 198.51.100.0/24
    Require not ip 203.0.113
</RequireAll>
The first line blocks 198.51.100.0 to 198.51.100.255. The second blocks every address starting with 203.0.113. For IPv6, use the full address or a prefix such as Require not ip 2001:db8::/32.
4. Allow Only Specific IPs
To lock a folder so only you and your developers can open it, use Require ip. Everyone else is denied automatically:
Require ip 203.0.113.25
Require ip 198.51.100.0/24
5. Use the Old Syntax on Apache 2.2
If apachectl -v shows Apache 2.2, use the original directives:
Order allow,deny
Allow from all
Deny from 203.0.113.10
Deny from 198.51.100.7
To allow only certain IPs on Apache 2.2:
Order deny,allow
Deny from all
Allow from 203.0.113.25
On Apache 2.4, these lines work only if mod_access_compat is enabled. Don’t mix them with Require lines in the same file.
6. Test the Rules
Save the file, then check the result from a blocked IP:
curl -I https://example.com
A blocked visitor should receive HTTP/1.1 403 Forbidden. Other visitors should still see 200 OK. Apache reads .htaccess on every request, so you don’t need to restart it. If you can’t test from the blocked address, check the log:
tail -f /var/log/httpd/error_log
On Debian and Ubuntu, the log is /var/log/apache2/error.log.
Troubleshooting
If you block IPs via htaccess and the rules do not work, check these:
- “500 Internal Server Error” after saving: The file has a syntax error. Restore
.htaccess.bak, then re-add the rules one at a time - “Invalid command ‘Require’, perhaps misspelled or defined by a module not included in the server configuration”: The server runs Apache 2.2, so use the syntax in Step 5
- “Order not allowed here” or “Allow not allowed here”:
AllowOverrideis too restrictive for the folder. Ask your host or setAllowOverride All - “AH01797: client denied by server configuration”: This log line is normal and shows that a block is working
- A blocked visitor can still open the site: You block IPs via htaccess but Apache sees the proxy’s address, not the visitor’s. This happens behind Cloudflare or a load balancer, so enable
mod_remoteipor block the IP at the proxy - You blocked yourself: Remove the rule through FTP, File Manager or SSH, or restore the backup
- The rules are ignored completely: The
.htaccessfile name has a typo, orAllowOverride Noneis set. Also confirm the file is in the correct folder
Conclusion
To block IPs via htaccess, open the file in the right folder, add Require not ip lines inside a <RequireAll> block (or Deny from lines on Apache 2.2), and test with curl. Use Require ip to allow only trusted addresses. Back up the file before every change, and use valid IP addresses, since an invalid one such as 290.0.0.0 never matches.
Frequently Asked Questions
Can I block IPs via htaccess on Nginx?
No. Nginx does not read .htaccess files. Use deny and allow rules in the Nginx server configuration instead.
How do I block a whole country or a range of IPs?
Use CIDR notation, for example Require not ip 198.51.100.0/24. For a whole country, a firewall or a service such as Cloudflare is easier, because country ranges are very long and change often.
Does .htaccess blocking slow down my site?
A few rules have almost no effect. Hundreds of lines are slower, because Apache reads the file on every request. For long lists, use a firewall such as iptables or firewalld.
Can I use the Order allow,deny lines from older guides?
They work on Apache 2.2, and on Apache 2.4 only with mod_access_compat. Use Require on Apache 2.4.
Related Articles
Setup redirection from one domain to another domain on .htaccess
How to redirect a website using .htaccess
Talk to Our Technology Experts
Dealing with spam bots, brute-force attempts, or suspicious traffic on your website? Our team can set up IP blocking, firewall rules, and ongoing threat monitoring to keep your site protected through our Security Services.
Connect with our technology experts.